

Reusable Credentials: Solving Workforce IAM’s Repeat Verification Problem
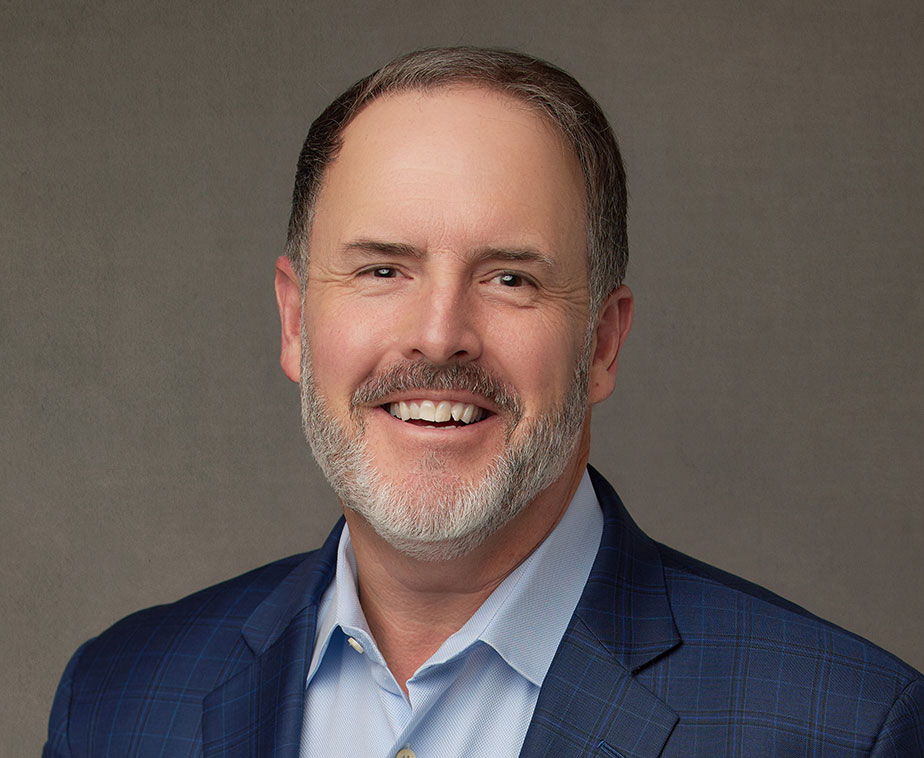
Bob Long
President, Americas
Bob is a tenured veteran in the Identity and eKYC global markets. In his present role at Daon, he has operational oversight for the Americas Region as President, including a seat on the Daon Board of Directors. Operational requirements include sales, business development, customer success, marketing, and operations for the region encompassing North America, South America, and Latin America.
Bob has over 25 years of experience in financial services, payments, fraud and risk management, and technology. Prior to Daon, he’s held the positions of Interim CEO and Chief Revenue Officer at a Seattle-based payment solutions company and led one of the largest payment and technology providers to an Initial Public Offering on the NYSE (2012). He has also held several leadership roles including Senior Vice President of Financial Services at Vantiv/WorldPay and leadership roles at both First Data Corporation and US Bancorp.
Bob received his education from the University of The Pacific in Stockton, CA.
October 29, 2026
Most workforce IAM programs verify identity repeatedly across recruiting, onboarding, and system access as if each previous check never happened, adding friction and cost without adding meaningful assurance. Reusable credentials only solve half the problem. What actually eliminates repeat verification is identity continuity: establishing high-assurance verification early and carrying it forward across every system and interaction rather than resetting at each new checkpoint.
Ask most identity and access management leaders when an employee’s identity verification process begins, and they will point to day one. Background check, badge issuance, credential provisioning: all of it starts the moment someone joins the organization. What happened before that moment, during recruiting, screening, or contractor onboarding, rarely factors into the system that will later govern that person’s access.
This is the quiet inefficiency sitting inside most workforce IAM programs. Identity gets proven, then proven again, then proven a third time, each instance treated as if the previous one never happened. A contractor verified during vendor onboarding gets re-verified for system access. A new hire confirmed during background screening gets re-confirmed during IT provisioning. Each step exists for a defensible reason. Together, they add friction, cost, and risk without adding much additional assurance.
The pressure to fix this is not new, but it has become harder to ignore. Compliance requirements are expanding across financial services, healthcare, and other regulated sectors. Fraud tied to synthetic identities and impersonation is rising in ways that make repeated, verification checks look increasingly fragile rather than protective. And a newer complication has entered the picture: organizations now need to govern not just human employees and contractors, but AI agents acting on their behalf or fraudulently, a category that traditional IAM and privileged access management frameworks were never built to handle.
Reusable credentials have emerged as a proposed fix. The concept is straightforward: verify someone once, at a high level of assurance, and let that verification travel with them across systems and touchpoints rather than resetting at each new checkpoint.
Reusability Is Not the Same as Continuity
Here is where the conversation tends to stall. A reusable credential, on its own, only solves half the problem. If the credential is portable but the identity behind it was never established with strength, or if there is no reliable way to confirm that the person presenting the credential today is the same person who was verified originally, reusability just moves the risk downstream instead of removing it.
What matters is not simply that a credential can be reused. What matters is that the identity underneath it is continuous: verified with confidence, tied durably to the individual, and carried forward across every system, platform, and interaction without having to be reconstructed from scratch each time. A credential that can be copied, shared, or presented by someone other than its original owner is not solving the workforce identity problem. It is just relocating it.
This distinction has a practical implication for where verification should happen. Most organizations still treat identity as something IAM systems handle after the fact, once someone has already been hired, screened, or granted vendor status. A more effective approach front-ends the work. Establishing a high-assurance identity earlier, during recruitment screening or initial account opening rather than at first system access, means every downstream step draws on something already verified instead of starting the clock over.
Why the Same Problem Shows Up Everywhere
This pattern is not unique to workforce IAM. Digital banking platforms run into a nearly identical version of it during account opening and know-your-customer checks, where fraud and risk teams are measured on keeping fraud ratios low while compliance teams are measured on avoiding regulatory penalties, two different mandates pulling on the same underlying identity question. Anti-money-laundering platforms and data aggregators face it from the investigative side, trying to confirm a human is who they claim to be before fraud has a chance to take root. Payment ecosystems face it at scale, with fraud losses across the industry running well into the billions annually.
Different departments, different KPIs, same root need: a verified identity that persists reliably enough to be trusted at every subsequent step, rather than one that has to be reestablished each time a new team or system gets involved. Agentic AI adds a new wrinkle to the same problem. Non-human identities acting on an organization’s behalf need to be established, authenticated, and governed with the same rigor as the humans who created them, and traditional credentialing systems were not designed with that requirement in mind.
What Continuity Delivers
The value of getting this right comes down to three qualities. Identity coverage that is more complete, spanning the full lifecycle from pre-employment or account opening through every subsequent interaction, rather than a single checkpoint that gets treated as sufficient on its own. An experience that is more compelling, because a verified identity that does not require repeated proof reduces friction for legitimate users while making it measurably harder for fraudulent ones to blend in. And a security posture that is more competitive, closing gaps that organizations relying on fragmented, checkpoint-based verification leave wide open across onboarding, authentication, and re-authentication.
Each of these plays out concretely. A bank that front-ends identity verification during account opening does not need to rebuild that confidence when the same customer later calls into a contact center or requests a step-up authentication for a high-risk transaction. A workforce IAM program that establishes continuity at the pre-boarding stage does not need to re-verify a contractor every time that contractor’s access scope changes. The assurance travels with the identity instead of resetting at each door.
The Strategic Case for Security Leaders
For CISOs, the appeal goes beyond convenience. Every additional verification checkpoint is also an additional point of potential failure, a place where a fraudulent actor might slip through, or where legitimate users get frustrated enough to look for workarounds that weaken security in practice. Reducing the number of times identity has to be reestablished narrows that attack surface.
There is also a broader shift underway in how security leaders think about their role. The traditional question, “is this the right person,” is giving way to a more continuous one: “can I trust that this is still the right person, acting appropriately, right now.” That shift moves organizations from establishing identity as a one-time gate toward approving activity as an ongoing discipline, a distinction that matters more each year as both the workforce and the systems accessing it grow more complex.
Where This Is Headed
Non-human identities are not a future consideration. Organizations are already deploying AI agents that need to be authenticated, authorized, and monitored with the same seriousness applied to human employees, and the identity frameworks capable of handling that will be the ones built on continuity rather than repeated point-in-time checks.
The organizations that treat identity as something continuous, established early and carried forward with confidence, will be the ones equipped to govern both their workforce and their expanding roster of digital agents without rebuilding trust at every turn. The ones still treating identity as a series of disconnected checkpoints will keep paying the cost of starting over, one verification at a time.